
Key Takeaways
- Securing SMS MCP tools means default-deny send, allowlisted destinations, env keys, and HMAC — not a first-party plugin we ship.
- list_devices can be read-only. send_sms is production IAM.
- Do not put OTP digits in tool arguments or results.
- Developer Center owns REST field names. Tools wrap them.
- BYO Android and operator credit. We meter devices and volume (Free 300 lifetime; paid from $19/mo).
Summary
Securing SMS MCP tools is the catalog: which verbs exist, who may call them, and what they are forbidden to echo. Concepts: securing tools concepts. Keys: auth and API keys. Spec: modelcontextprotocol.io. REST: Developer Center.
If send_sms takes a free-form destination, you did not ship a tool. You shipped a programmable SIM with a chat UI.
Every tool is an IAM role
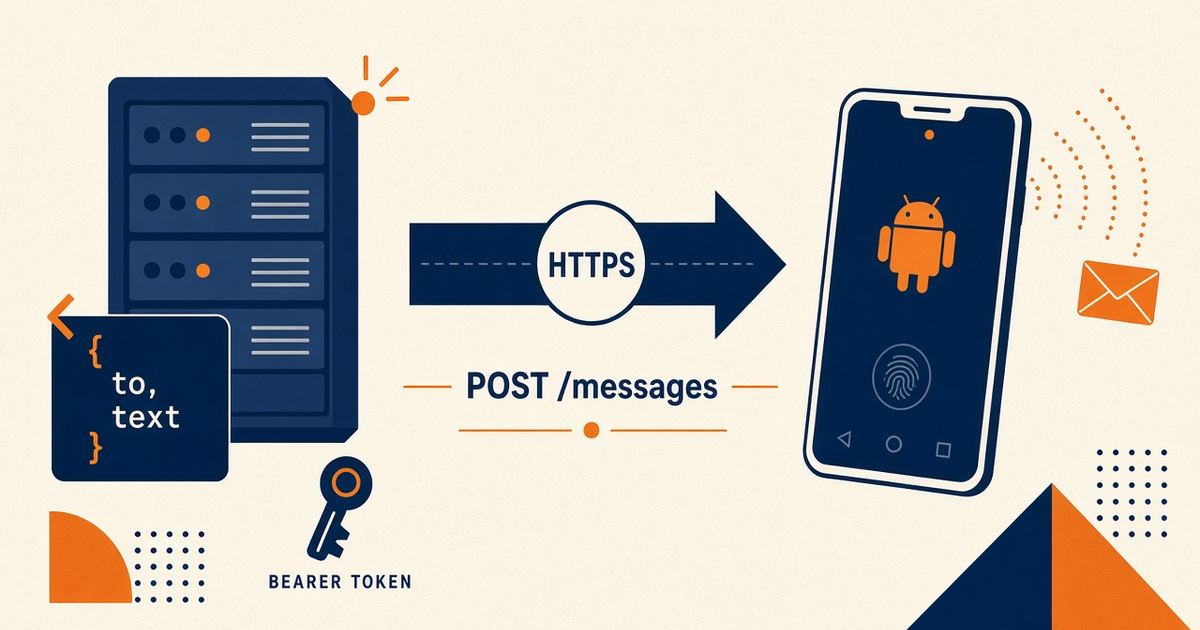
The adapter is not an SMSC. Recipients still see your MSISDN. How the gateway works. No first-party plugin.
Context
Demo catalogs enable everything. Production catalogs enable almost nothing. Pairing stays in setup.
Harden the catalog
- Default-deny send. Allowlist destinations in the server, not in the prompt.
- Split canary_send from bulk_send. Keep bulk off the agent host.
- Idempotency keys from a business id.
- Redact bodies in results. Return message ids.
- HMAC-verify inbound before any tool that sends.
Default posture
| Tool | Staging host | Production agent |
|---|---|---|
| list_devices | On | Read-only key |
| canary_send | Allowlisted | Staff only |
| send_sms open dest | Off | Off |
| create_webhook | HMAC required | HMAC required |
Open send is an airtime leak
Each accept spends operator SMS and platform volume. Devices and volume. Rate-limit in the adapter.
Operations
After host updates, dump the enabled tool list. Last-seen on the handset is still the uptime signal.
HMAC before side effects
Verify signatures on the raw body. Do not document bypasses. Fail closed. Webhooks.
Decision guide
Ship a tiny catalog. Add verbs only with an owner and an allowlist. Customer OTP stays on the product REST path.
Checklist
- Open send off.
- Env keys; not mcp.json.
- HMAC on inbound.
- Bodies redacted.
- No first-party plugin claim.
Next steps
Cursor host: Cursor MCP setup security. Logging: logging and audit.
Related product pages
Jump to the live product docs for this topic—not another long-form article.
- SMS API documentationLive endpoint reference
- device and SMS volume pricingPlans and allowances
- Security and Trust CenterCompliance and posture
- Android SMS gateway product guideDefinition, product, and how to buy